Today we are rolling out a major upgrade to how rules work in ZERO-PROTECT, our BSI-qualified DDoS protection and WAF for websites and APIs. It is built for the people who run sites and APIs every day: exceptions exactly as wide as you need them, complex policies in a single rule, and a plain-language summary under every rule. Live for every customer in the portal, with nothing to migrate.
Exceptions, Exactly as Wide as You Need
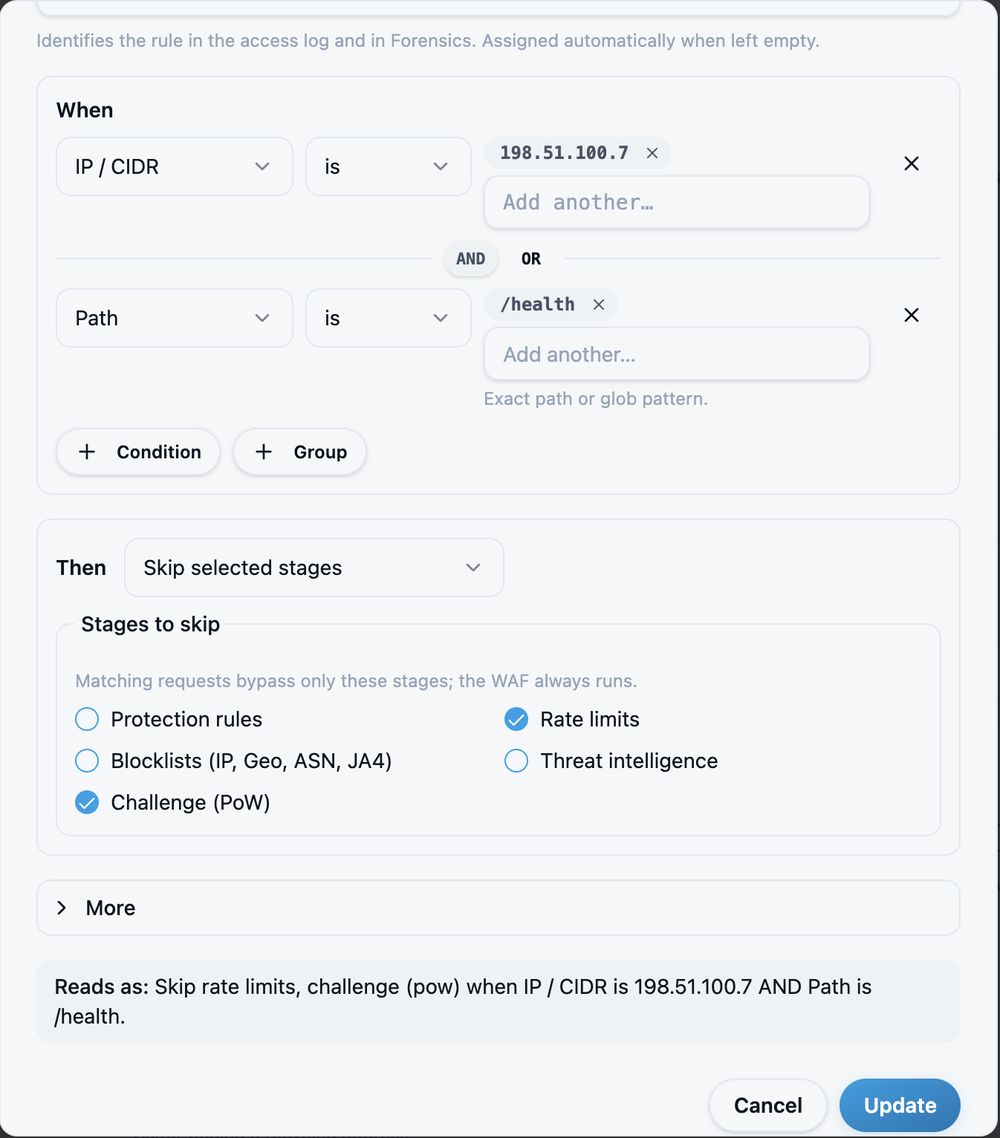
The new skip action lets you choose which protection stages an exception bypasses. Your uptime monitor skips the challenge and the rate limits, and everything else keeps working for it: blocklists, threat intelligence, your other rules. The WAF always runs.
One rule, one purpose, and the rest of your protection stays in place.
Complex Policies in a Single Rule
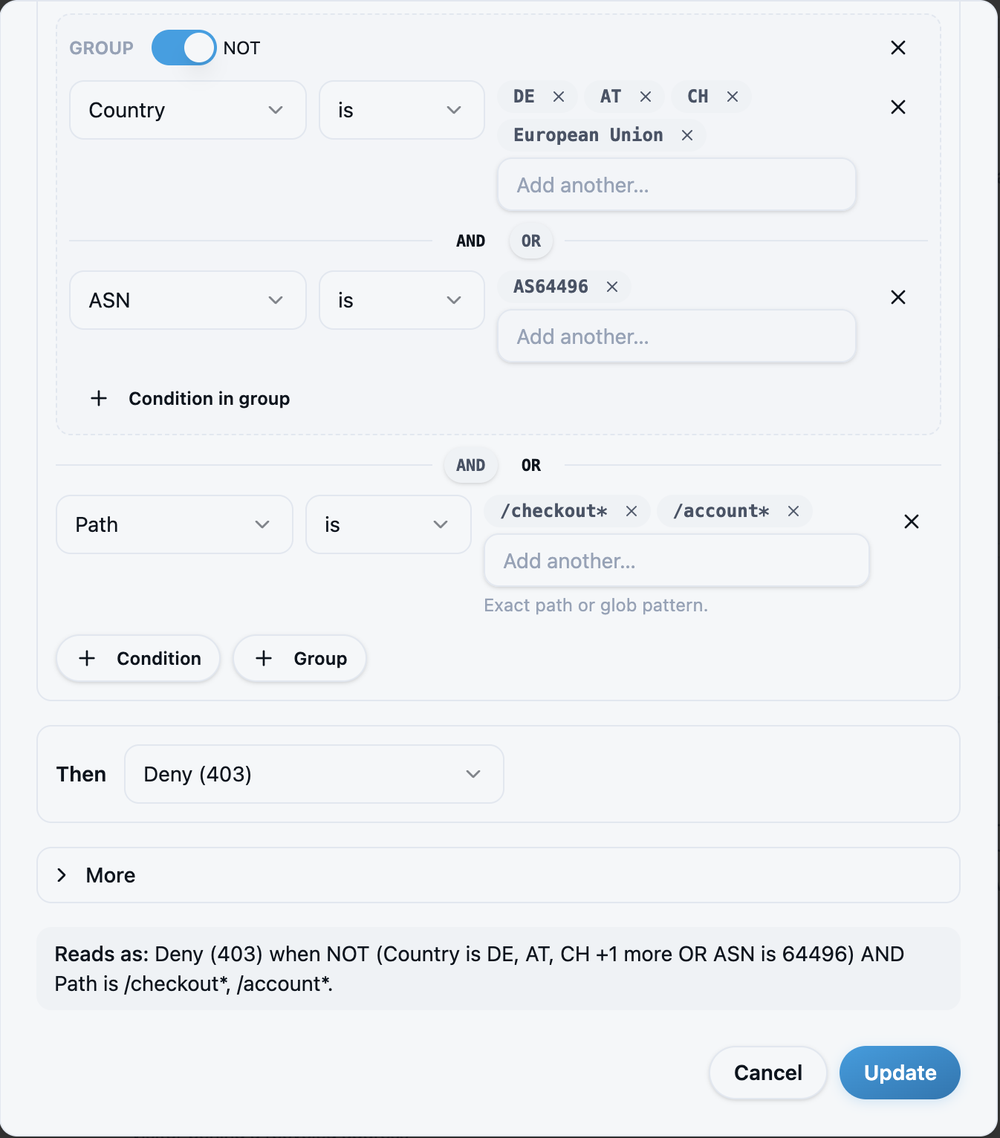
Conditions can now be grouped and combined with AND and OR inside one rule. "Allow our markets or our partner network, but only enforce it on checkout and account pages" is a single rule instead of a carefully ordered set.
Fewer rules, less to keep in your head, and the logic sits exactly where you expect it.
Every Rule Explains Itself
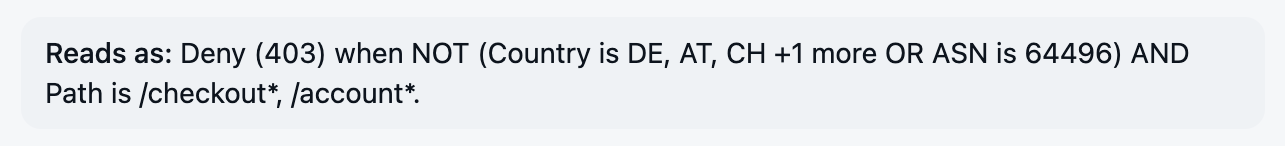
Below every rule, the portal spells out in one sentence what it does. You read your policy the way you would explain it to a colleague, and you confirm it before it goes live.
Nothing to Migrate
Your existing rules keep working exactly as before, allow included, and flat rules stay valid in the API. When you next touch an exception, give skip a try, and if a policy is spread across several rules today, it probably fits into one now.
Every field, action and example is in the protection rules documentation.